
Sydney Guides: Sydney for Students
A comprehensive guide to Sydney for students, including universities, accommodation, and costs. Sydney is home to some of Australia's most prestigious
7 min read
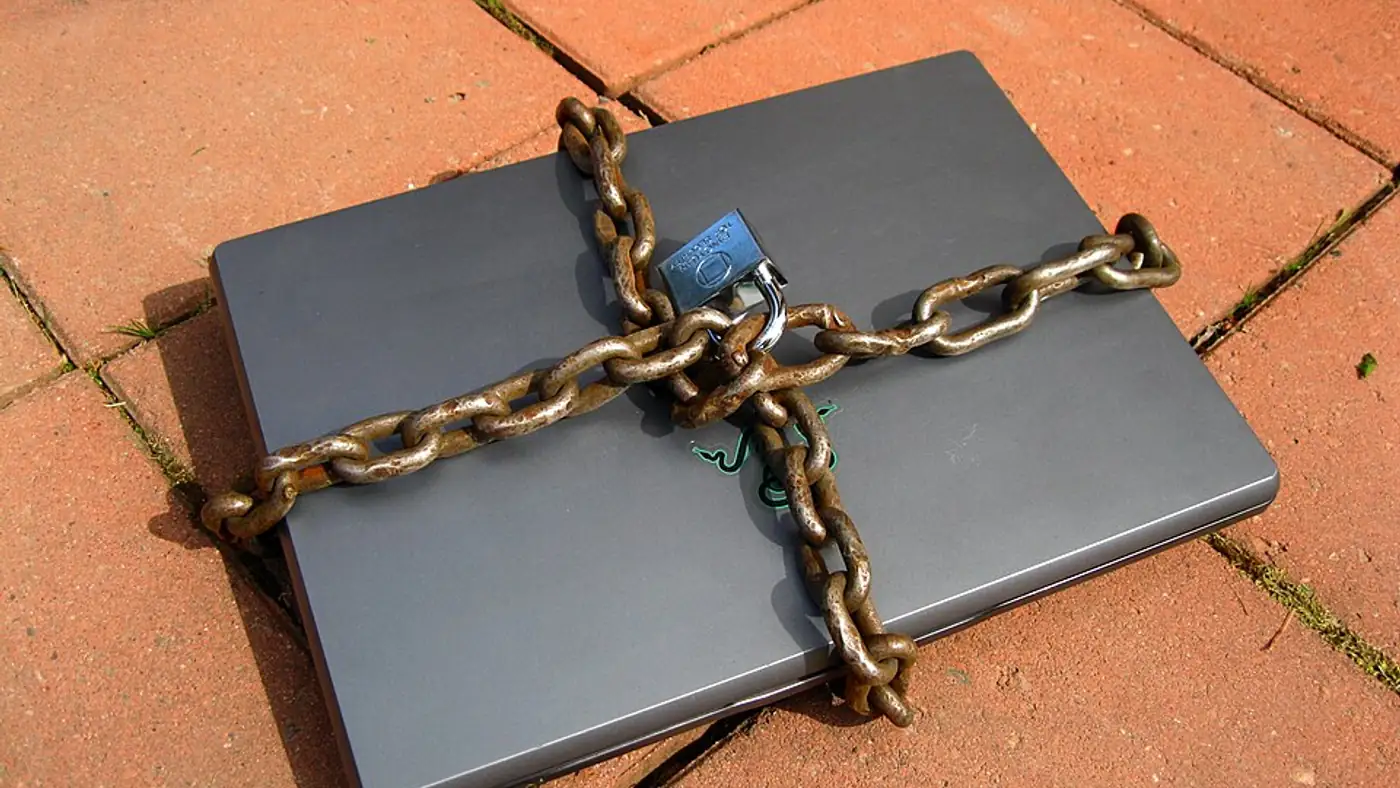
A realistic weekend cyber security checklist for Sydney small businesses: multifactor authentication, backups, patching, staff habits and an incident plan
The Guides Desk is a contributing writer covering guides and public affairs for The Sydney Times.
Australian small businesses are being targeted at a scale that rarely makes the news cycle. The Australian Signals Directorate's reporting consistently shows small and medium organisations making up the largest share of reported incidents, and the dominant entry points are unremarkable: an invoice attachment, a password reused from a personal account, an old laptop that was never patched.
The good news is that most of those paths close with a weekend of work. This checklist is ordered by how much risk each step removes per hour spent.
Write down what the business actually runs on. Every system a staff member needs to do their job: accounting, payroll, quoting, customer records, email, file storage, website, booking system. For each one, note who has access, where the data lives, and what would happen if it disappeared for three days.
This inventory takes ninety minutes and it is the foundation for everything below. A backup strategy built without an inventory is guesswork.
Turn on multifactor authentication for every account that matters, starting with email. Email is the single highest-value account in a small business because it is the reset path for everything else. If an attacker controls the mailbox, they can reset the bank account.
Use an authenticator app or a hardware key rather than SMS where the platform allows it. SMS codes are better than nothing and materially better than a password alone. A hardware key is roughly $40 per seat and is the strongest cheap option for finance and executive accounts.
Then audit the accounts nobody uses any more. Shared accounts that outlived their owner are a common finding. Remove them, or at minimum, rename and attach multifactor authentication.
Require automatic operating system updates on every device that touches business data. Automatic updates is a setting, not a project. Do it on laptops, desktops and phones.
Check what personal devices are in use. Staff with company email on personal phones is normal and reasonable, but it needs a written rule about what is permitted. Remote wipe capability on company phones is worth having in the written policy even if you rarely use it.
Train on two behaviours only. First, verify any payment or bank-detail change by a second channel, using a phone number already held rather than one supplied in the email. Second, treat unexpected attachments as hostile until checked. Both behaviours prevent the majority of incidents reported to small businesses.
Three things matter and none of them is "we have a cloud subscription."
The backup must be separate from the original. Ransomware will encrypt synchronised folders, and if your backup is in the same sync tree it will be encrypted too. Three copies, two media types, one offsite is the standard rule.
The backup must be tested by restoring. A restore test once a quarter, on a random file set, tells you whether the backup is real.
Access to the backup must be separate from normal day-to-day credentials, and it should be protected by multifactor authentication.
Write a one-page incident plan. Who to call, in order. That page should include your bank, your insurer, your IT provider, and the national reporting line. Keep it printed and offsite.
Reporting requirements have tightened in recent years, and Australian cyber crime reporting obligations now include a duty for entities to report ransomware and certain other incidents to the national cyber security coordinator. A written plan is what makes that possible under pressure.
Insurance is worth reading properly. Cyber policies vary widely on whether they cover business interruption, data restoration costs, and the incident-response retainer. Know your excess before you need it.
Saturday: the inventory, then multifactor authentication on email and finance accounts, then automatic updates on every device. Sunday: backups, separated and tested, then the one-page incident plan, then the two staff behaviours written down and explained.
That is the list. It is not a complete security program, and it will not stop a determined attacker with a valid credential. It removes the overwhelming majority of the paths that small businesses actually lose through, which is a good weekend's work.
For more Sydney business guides, see Business.
Direct inquiries, corrections, or documentation concerning this dispatch to our editorial newsroom desk.
A comprehensive guide to Sydney for students, including universities, accommodation, and costs. Sydney is home to some of Australia's most prestigious

A comprehensive guide to Sydney for families, including schools, parks, and activities. The city offers an exceptional range of family-friendly

A comprehensive guide to moving to Sydney, including neighbourhoods, transport, and costs. The guide covers everything you need to know about relocating

A comprehensive guide to navigating Sydney, including transport, neighbourhoods, and essential tips. The guide covers everything you need to know about